
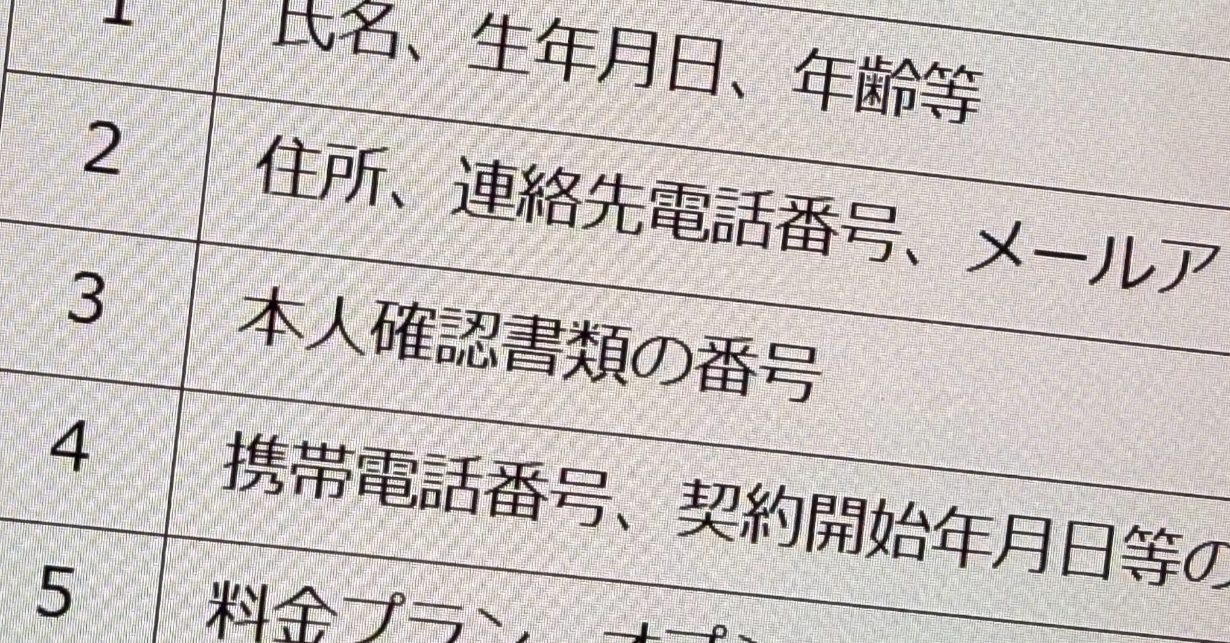
NTT Docomo said on November 6 that identity-verification document numbers were among the customer data exposed in unauthorized access to its My docomo and Docomo Online Shop services, which affected up to 300,000 records, and that it is considering compensation payments to users.
The figure covers 204,157 individual customers and 90,682 corporate ones.
In its first disclosure on November 5, the carrier listed names, addresses, dates of birth, mobile phone numbers and contact phone numbers as leaked, and said the cause was under investigation. It has since widened the list of exposed items and stated that the cause was unauthorized access.
What was exposed
Across all affected records, Docomo added identity-verification document numbers, contract information such as the contract start date, contract details including rate plans, options and discounts, and age and email address.
For some customers, the following also leaked:
- Financial institution name, branch name, account number and account holder name
- Names and contact details of legal representatives and procedural representatives
- Employer or corporate name and location
- Information related to the child-rearing support program
Docomo said it is still investigating how the intrusion occurred and the scope and volume of the leaked information.
Services still down
The company confirmed unauthorized external access to both sites on November 4 and suspended procedures from around 1:05 a.m. on November 5. No date has been set for restoration.