
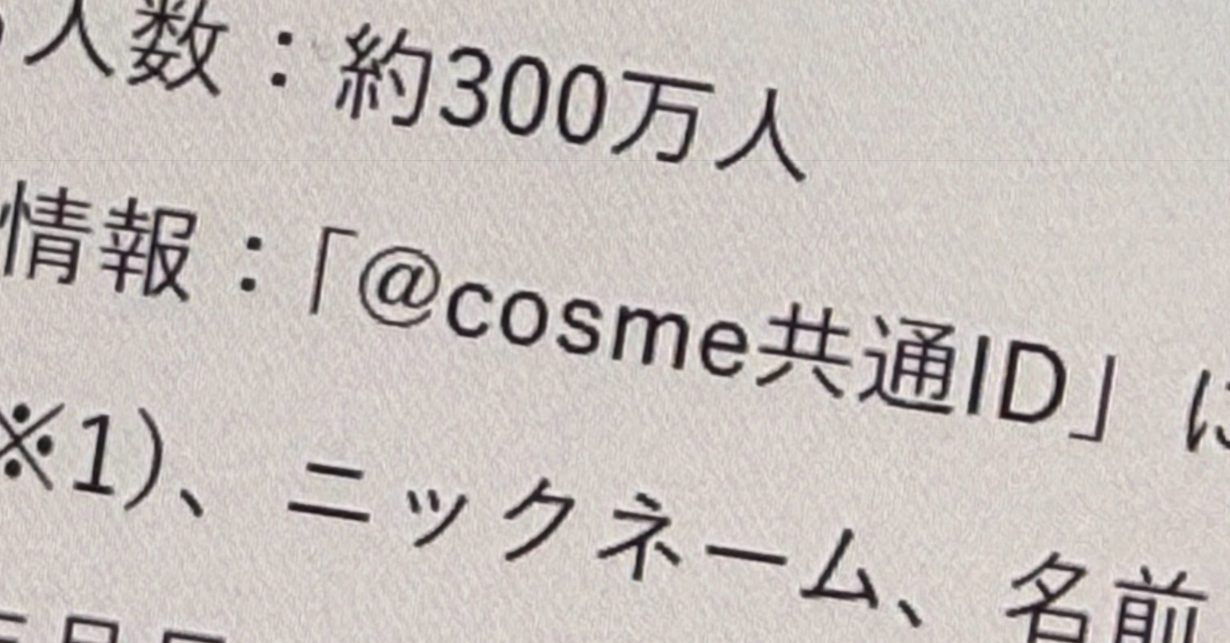
Istyle, the company behind the cosmetics site @cosme, said on November 2 that unauthorized access by a third party had leaked the data of about 3 million members registered under the site's common ID.
The leaked data includes names in kanji and kana, postal codes, addresses, phone numbers, email addresses, automatically issued user IDs, gender, dates of birth, nicknames, skin type and hair type. Istyle said it has confirmed that login passwords and credit card details are not among the data.
The company confirmed the leak on October 28. It has not disclosed when the unauthorized access took place or how it was carried out. People who have since closed their accounts are affected if they were members at the time of the access.
Investigation and notification
Istyle has brought in an outside security firm to establish the cause and the scope of the damage. It will consider and implement measures to prevent a recurrence based on the findings.
The company will contact affected members individually through the contact details it holds, and expects to finish reaching them by November 6. The notification emails will come from the cosme.net domain. Former members will be contacted using information kept for a set period after closure under the company's privacy policy.
The disclosure follows a run of leaks at Japanese services, including a breach at a GMO group single sign-on service that exposed data on 45,000 people and a credential-stuffing attack on Japan Post's Yu ID.