
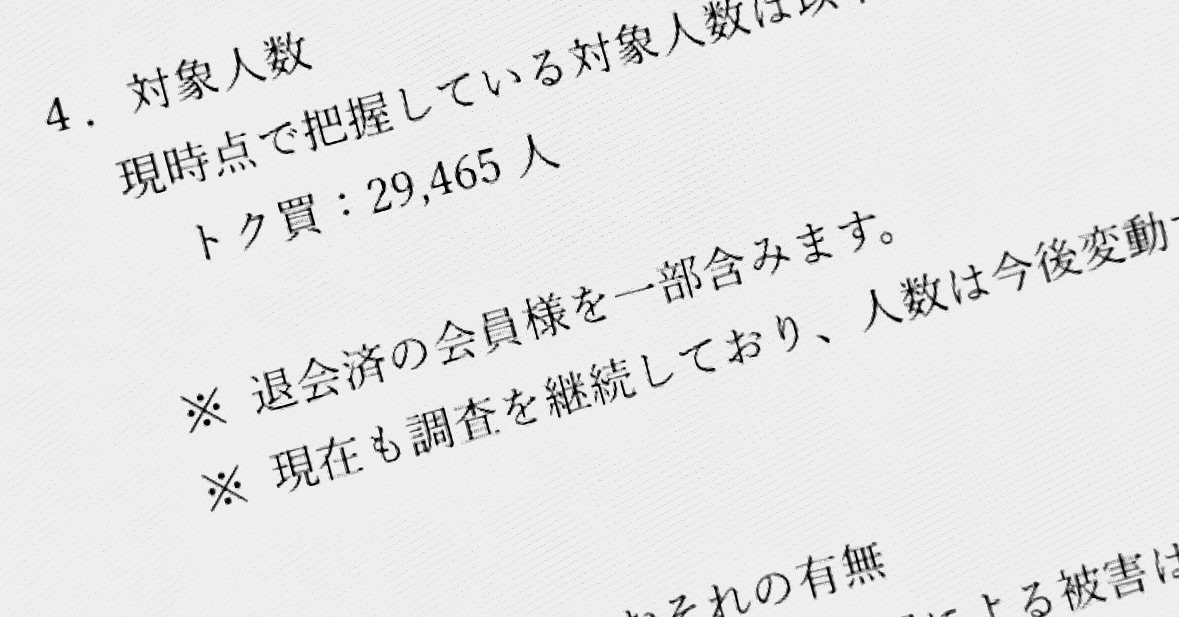
Benefit One, a Tokyo employee-benefits provider, said on Oct 28, 2026 that intruders broke into a system run by its contractor Forestec and exposed the personal data of 29,465 members of Tokubai, a discount service for Credit Saison cardholders. Some of the authentication information Benefit One uses to connect to a payment system may also have leaked, the company said.
The intruders accessed Forestec's system repeatedly between Oct 14 and Oct 20, 2026. Forestec detected part of the activity on Oct 21 and reported it to Benefit One, which suspended Tokubai the same day. More intrusions were detected on Oct 24 and Oct 25. The cause is still under investigation.
The exposed records include names, phonetic readings of names, dates of birth, gender, postal codes, email addresses, customer numbers, join-and-leave records and administrative numbers used to process membership-fee payments. Which fields apply varies by member depending on what each person registered, and some of those affected have already cancelled their memberships.
Not a Saison breach
Tokubai is operated jointly with Credit Saison, and Benefit One said the leak did not come from systems managed by the card issuer. Benefit One plans to restart the service once it has identified the cause and finished measures to prevent a repeat.
The company is contacting affected members at their registered email addresses in turn and warned them to watch for suspicious messages posing as notices from Benefit One or its partners.
Second leak in a month
Benefit One disclosed another breach on Sept 30, 2026, when personal data on 13,460 people leaked through Benewan Platform, a service for staff at client companies and organizations. That incident stemmed from a misconfiguration in a feature that downloads survey results.
Outsourced systems have been a recurring weak point in Japanese corporate breaches. Bandai Namco reported in 2026 that email addresses for 340,000 members of a Gundam merchandise point program leaked after an intrusion at its email vendor Yumirink, and NEC apologized after a breach at one of its contractors.